Insurance Posture Management: Proof Your Policy Holds
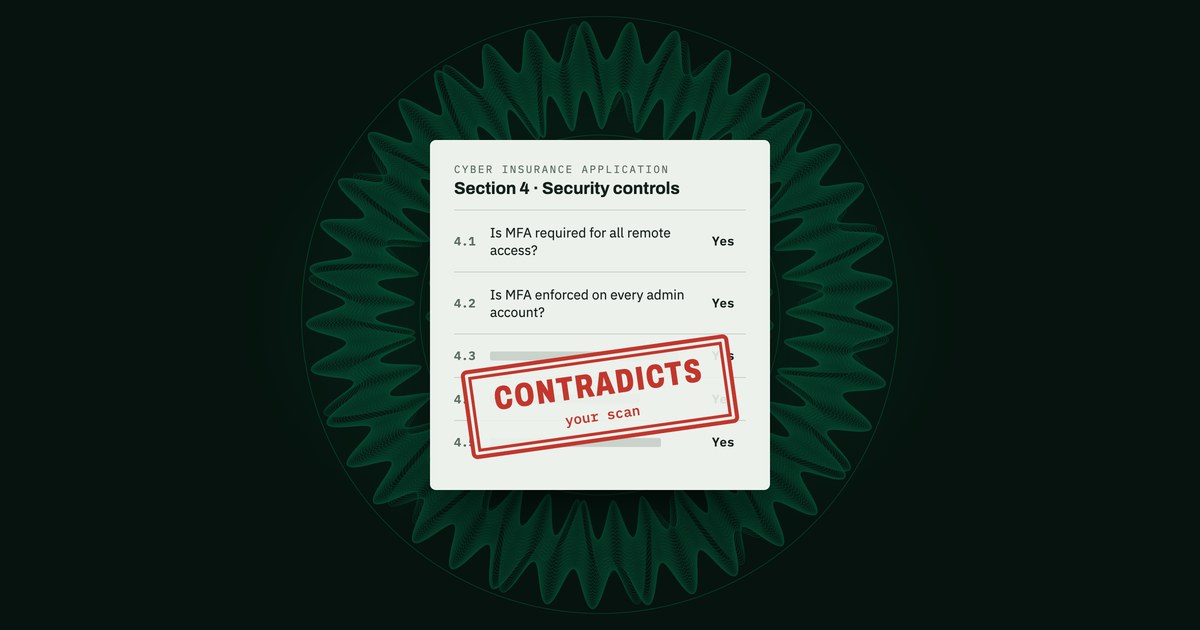
Insurance posture management checks your cyber insurance answers against real scans. Why it belongs in GRC, and what the Hamilton denial teaches.
Expert perspectives on cloud security, compliance, and threat intelligence. Practical guidance for security leaders navigating an evolving landscape.
 Compliance
Insurance posture management checks your cyber insurance answers against real scans. Why it belongs in GRC, and what the Hamilton denial teaches.
 Compliance
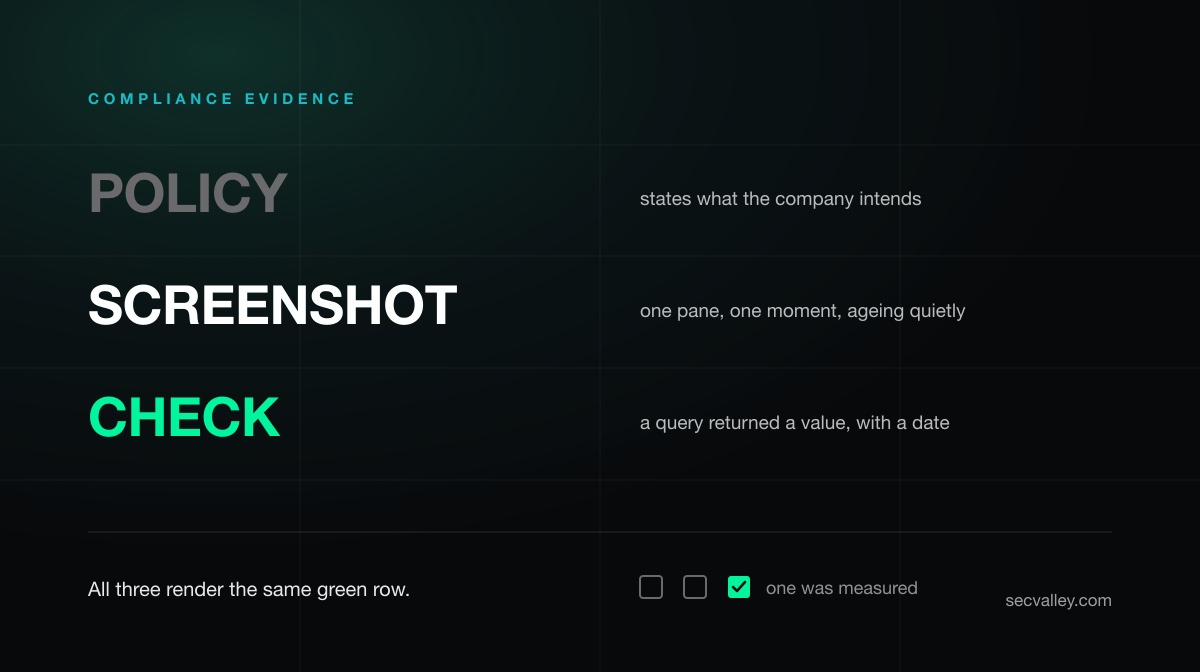
A green compliance row means a requirement was mapped to a document, not that a query read your tenant. Only one of those claims survives an incident.
 Compliance
SOC 2 evidence is a dated record that a control ran inside the window, not a screenshot of today's dashboard. What auditors sample, and why green is not proof.
 Compliance
Cloud compliance means your cloud systems meet regulatory standards and security policies. Key frameworks like SOC 2, ISO 27001, HIPAA, GDPR, and how CSPM helps.
 Compliance
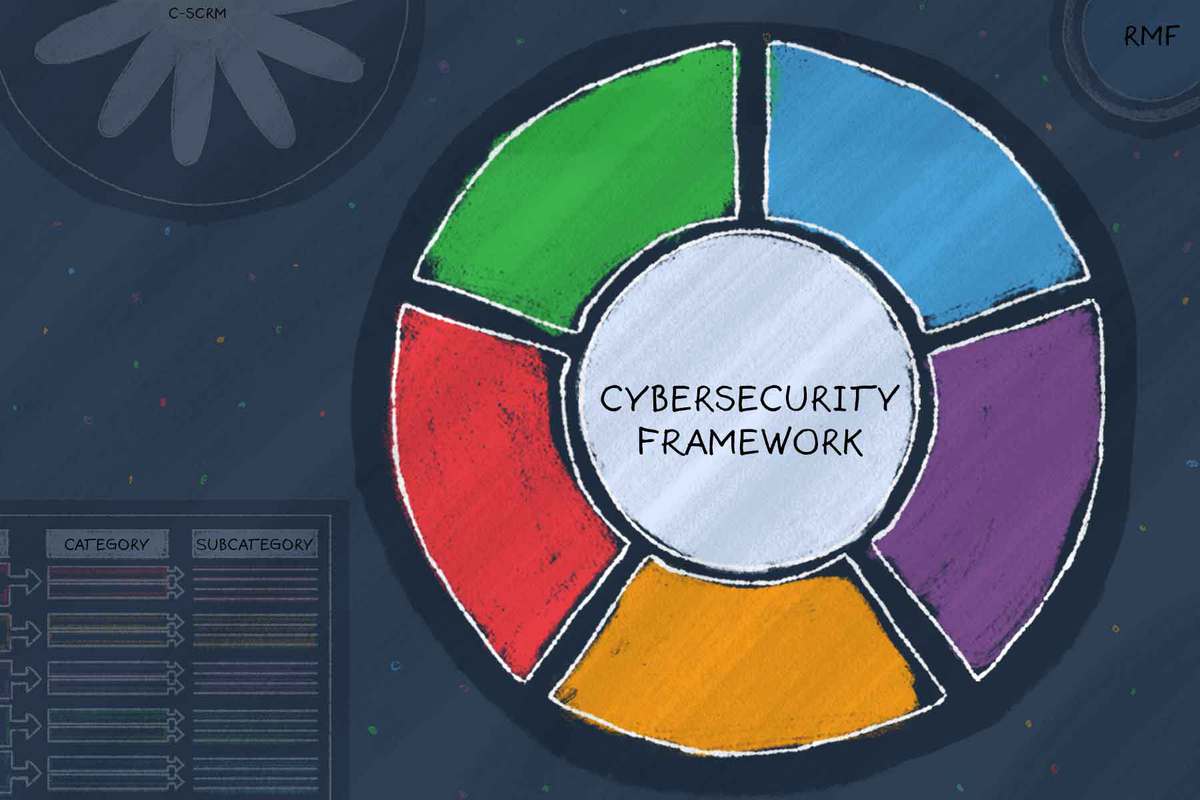
The NIST Cybersecurity Framework gives you a practical structure for security. Here's how to actually use it without drowning in documentation.