Interactive vs Non-Interactive Sign-Ins in Entra ID
Interactive vs non-interactive sign-ins in Entra ID: what each one means, how to read the last non-interactive sign-in field, and where a stolen token hides.
Expert perspectives on cloud security, compliance, and threat intelligence. Practical guidance for security leaders navigating an evolving landscape.
 Cloud Security
Interactive vs non-interactive sign-ins in Entra ID: what each one means, how to read the last non-interactive sign-in field, and where a stolen token hides.
 Cloud Security
Microsoft is retiring SharePoint OTP sign-in for external users by the end of November 2026. What breaks, how guest access comes back, and why your guest list grows.
 Cloud Security
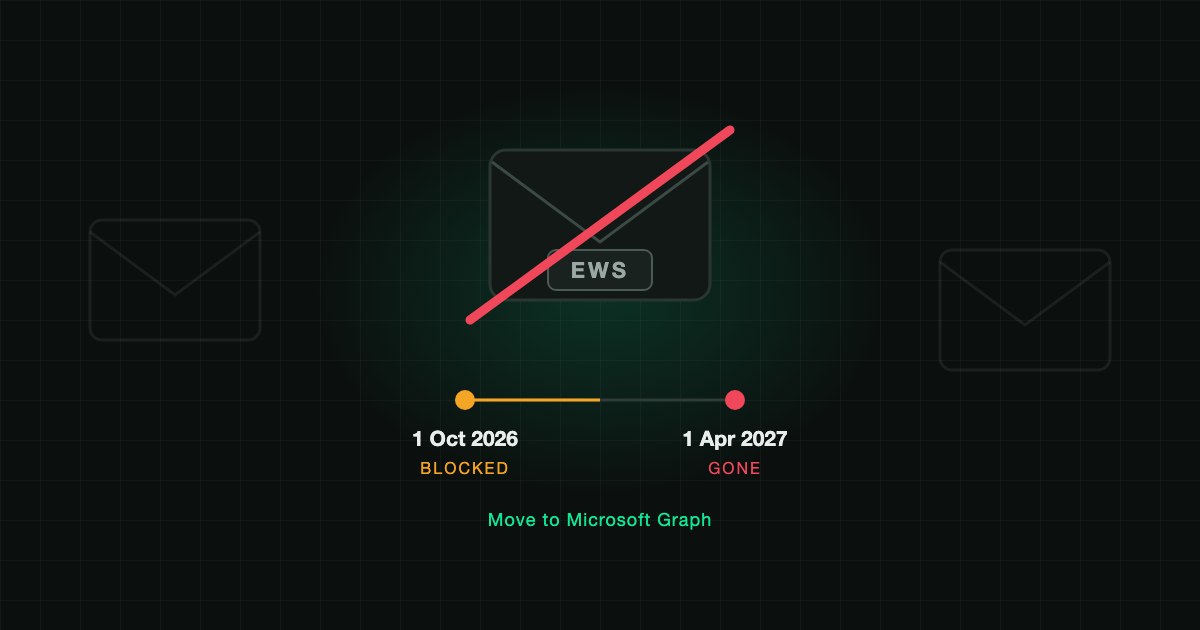
Microsoft began blocking Exchange Web Services (EWS) in Exchange Online on 1 October 2026 and removes it for good on 1 April 2027. How to find every app still calling EWS, how the EWSAllowedAppIDs allow list works, and why EWS access is a security finding, not just a migration task.
 Cloud Security
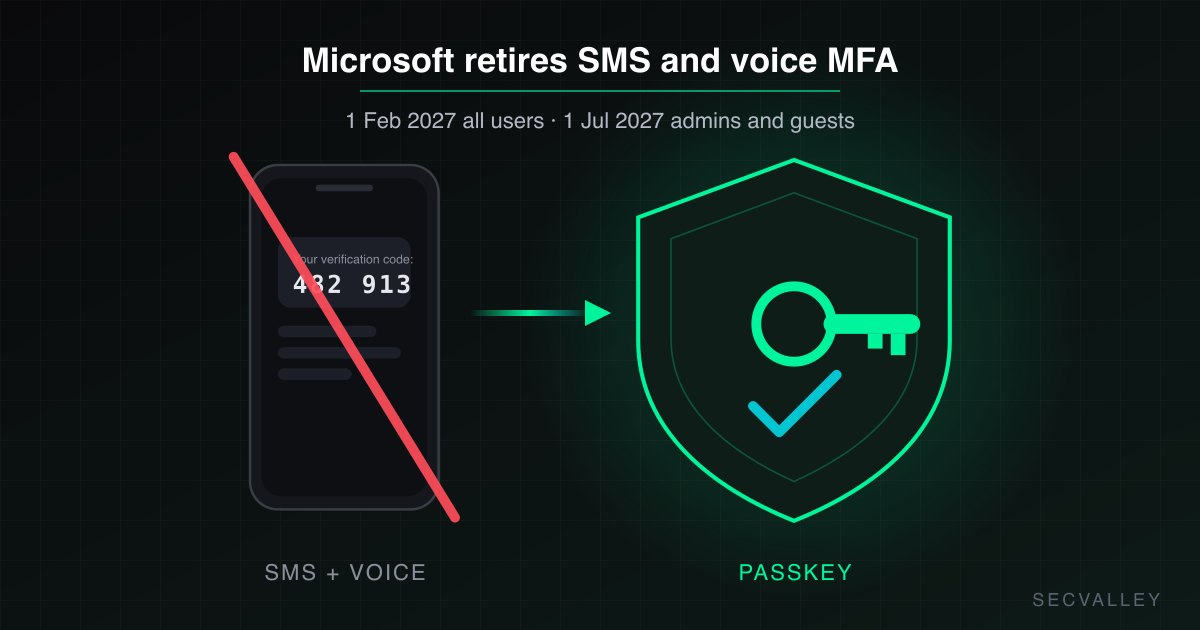
Microsoft retires SMS and voice call authentication on 1 February 2027, with Global Administrators and guests following on 1 July 2027. No opt-out, MFA and password reset alike. How to find every phone-only user in Entra ID and move them before sign-in breaks.
 Cloud Security
Every AI agent and Copilot extension becomes an Entra ID service principal with standing permissions and no MFA. How to inventory them before they outlive owners.
 Cloud Security
CIS AWS Foundations v7.0.0 asks for 15 CloudTrail monitoring alarms. The full list with control IDs, which five to build first, and why scanners skip them.
 Cloud Security
Non-interactive sign-ins are logins performed on your behalf by an app or a token, and Entra ID hides them on a separate tab most people never open. That is exactly where a stolen session token reuses your identity after MFA is already satisfied.
 Cloud Security
Microsoft 365 Copilot did not create your oversharing problem. It inherited a decade of it and gave every employee a conversational way to surface it in seconds. Here is why Copilot exposes latent access risk, and how to govern it before rollout.
 Cloud Security
Every external collaboration adds a guest to your Microsoft Entra ID tenant, and almost none ever leave. Why guest sprawl is so common and so often ignored.
 Cloud Security
Storage accounts are where the data actually lives, which makes them the first thing attackers go after. After auditing hundreds of Azure subscriptions, the same six exposure patterns keep showing up.
 Cloud Security
Key Vault is supposed to be the safe place for your secrets. After auditing hundreds of Azure subscriptions, the same misconfigurations keep showing up.
 Cloud Security
Power Apps and Power Automate let anyone in your tenant build apps that touch sensitive data. Here is how citizen development becomes the new shadow IT.
Page 1 of 3